AI Agent Governance for Secure Enterprise AI Adoption
Deploying AI Is Only the Beginning. Governing It Is What Makes It Enterprise-Ready.
AI agents are moving from experimentation into business operations. But without clear ownership, controlled access, and effective oversight, AI agents can introduce risks faster than organizations can manage them.
TechDemocracy works with enterprises to establish the governance, identity security, and risk controls needed to adopt AI agents responsibly and scale with confidence.
Schedule a consultation
AI Adoption Is Outpacing Governance
Organizations are adopting AI across business functions, but visibility and control often lag behind.
Some are preparing to deploy their first AI agents. Others already have agents operating across applications, data, and workflows, but they lack a complete picture of access and ownership.
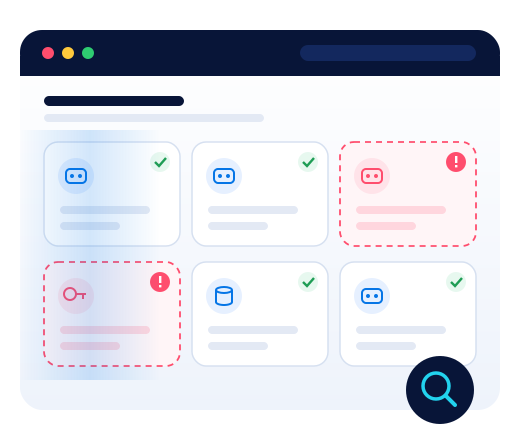
Without effective AI agent governance, organizations risk:

Shadow AI and unapproved agents operating outside established controls.

Excessive permissions and exposure of sensitive data.

Unmanaged identities, credentials, and service accounts.

Autonomous actions without clear accountability.

Governance gaps that hinder secure enterprise-wide adoption.

The challenge isn’t simply adopting AI. It’s understanding what your AI agents can do, what they can access, and who is accountable for their actions. Unlike traditional human identities, AI agents introduce a new level of risk, where the consequences of inadequate governance can be far greater. Getting this right isn’t optional.
From AI Experimentation to Governed AI Operations
Responsible AI adoption requires more than policies or a security tool. Governance must connect business accountability with technical controls.
 01
Discovery and risk
Identify AI agents, map their connections and permissions, and prioritize risk.
 02
Governance
Define policies, ownership, approvals, risk classifications, and human oversight.
 03
Identity security
Govern AI agents, machine identities, service accounts, and their access privileges.
 04
Monitoring and accountability
Establish visibility into agent activity and the controls needed for ongoing oversight.
AI Agent Governance Services from TechDemocracy
Whether your organization is planning its first AI agent or already operating agents across the enterprise, TechDemocracy helps you identify the right starting point.
 01
AI Agent Governance Foundation
Establish the policies, processes, roles, and security requirements needed to introduce AI agents responsibly.
Governance framework, agent approval, risk classification, identity standards, and implementation roadmap.
The organization that is beginning its journey and is just starting to deploy AI into their environment.
 02
AI Agent Governance Rapid Assessment
Evaluate existing AI adoption and governance maturity to identify control gaps, priority risks, and practical next steps.
Current-state assessment, known agent inventory, governance gaps, and prioritized roadmap.
For organizations with existing AI deployments seeking a comprehensive AI inventory, governance policies, and a strategic roadmap for effective AI governance.
 03
Enterprise AI Agent Discovery and Risk Assessment
Identify known, unmanaged, and potential shadow AI agents while examining their identities, credentials, connections, and effective access.
Technical discovery, agent-to-identity mapping, permissions analysis, and risk-based remediation priorities.
For organizations seeking to identify unmanaged or shadow AI agents, assess their identities, permissions, system access, and associated risks, and establish a risk-based remediation plan to strengthen security and governance.
What Enterprise Leaders Gain
For CIOs, CISOs, CTOs, and risk leaders, AI agent governance is a business and security priority, not just a technology exercise.

Reduced AI risk
Identify risky access, unmanaged agents, and gaps in oversight.

Clearer accountability
Establish ownership and approval requirements for AI-driven actions.

Stronger identity security
Bring agent identities, credentials, and access privileges into the governance model.

A practical path to scale
Prioritize actions and build a roadmap aligned with business objectives and risk tolerance.
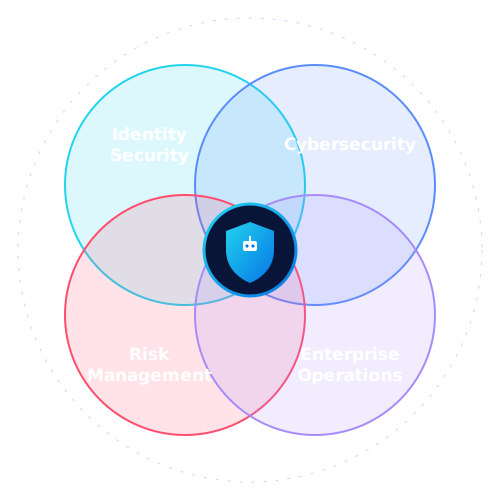
Why TechDemocracy for AI Agent Governance?
AI agent governance sits at the intersection of identity security, cybersecurity, risk management, and enterprise operations.
TechDemocracy brings these disciplines together through an approach built around:

Identity-first security: govern the identities and access behind AI-driven actions.

Governance by design: define ownership, approvals, and controls from the outset.

Risk-led discovery: identify visibility gaps and prioritize the risks that matter.

Enterprise readiness: align governance with existing security architecture and business objectives.
The goal is not simply to enable more AI. It is to help organizations adopt AI agents with the visibility, controls, and accountability required to operate them confidently.
Your AI Strategy Needs a Governance Strategy
AI agents are becoming part of enterprise operations. The question is whether your organization has the visibility, identity controls, and governance framework to manage them.
TechDemocracy can help you establish a clear path toward secure, accountable, and scalable AI adoption.
Talk with the TechDemocracy team about your AI agent governance, security, and discovery priorities.