LatestThe Secret Zero Problem: The First Credential Attackers Target
Resource / Online Journal
Challenges in Integrating AI into Workflows: Identity Security Playbook
Explore practical strategies for overcoming the hurdles of integrating AI into your workflows. Read the article to enhance efficiency and effectiveness.
Published on Oct 15, 2026
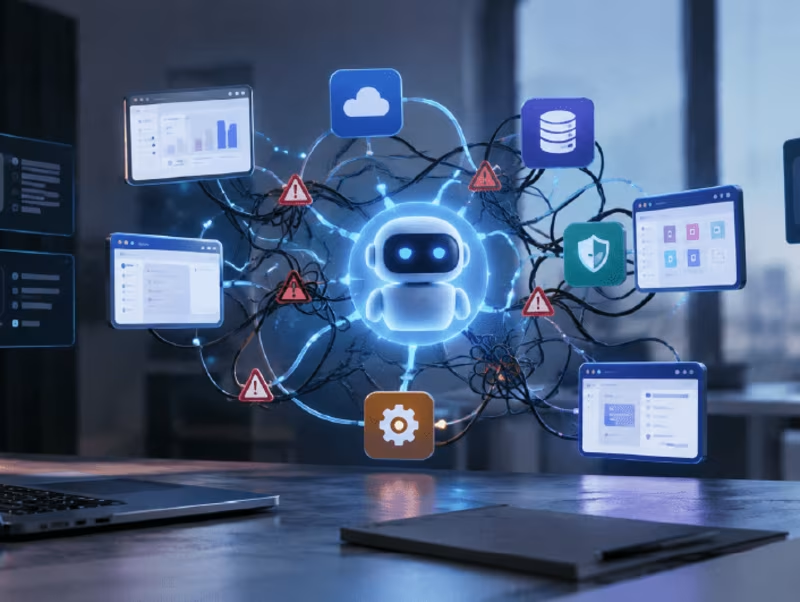
AI development has advanced so far that businesses are integrating AI into their workflow; some of these include customer service, software development, security operations, identity management, and business decision-making. Yet many AI projects fail to move beyond pilots. The problem is rarely the technology itself. More often, it comes down to governance gaps, poor data quality, unclear ownership, and security risks.
A recent industry study found that while most organizations are exploring or deploying AI, only a small percentage have mature AI governance practices in place. This creates significant challenges around accountability, traceability, data management, and regulatory compliance.
So, what are the biggest challenges organizations face when integrating AI into business workflows?
Common Challenges in Integrating AI into Workflows
1. Weak AI Governance and Accountability
Many organizations rush into AI adoption without establishing clear governance policies. Teams deploy AI tools to improve productivity, automate tasks, or support decision-making, but nobody defines who is accountable when something goes wrong.
Consider a customer support chatbot that provides inaccurate information or an AI agent that makes an unauthorized workflow decision. Without documented governance policies, organizations struggle to determine responsibility, investigate incidents, and meet audit requirements.
Before deploying AI, organizations should define governance frameworks, approval processes, risk classifications, and accountability structures. Every AI workflow should have a clearly identified owner responsible for compliance, monitoring, and business outcomes.
2. Data Privacy and Regulatory Risk
AI systems rely heavily on data. The challenge is ensuring that sensitive information is handled appropriately throughout the workflow lifecycle.
For example, an employee may upload customer data into a public AI tool to generate reports. While the action seems harmless, it can introduce privacy, compliance, and intellectual property risks.
Organizations must document data flows for every AI use case and determine:
- What data is being accessed?
- Where is the data stored?
- Who can access it?
- How is it being retained and audited?
As regulations continue to evolve, CISOs and CIOs should prioritize AI initiatives based on both operational value and regulatory exposure.
3. Poor Data Quality Produces Poor Results
According to The Guardian, a leading Wall Street law firm submitted court documents containing AI-generated false legal citations and misquotes, exposing failures in human review and AI oversight.
Organizations frequently discover that their data is fragmented across applications, contains duplicate records, or lacks proper classification. As a result, AI-generated insights become unreliable.
Imagine an AI-powered identity governance system making access recommendations based on outdated employee records. The automation may increase efficiency while simultaneously increasing security risk.
Successful AI integration requires strong data governance, standardized data management processes, and continuous validation of data sources.
4. Integration Complexity Across Existing Systems
Many enterprises operate hundreds of business applications that were never designed to work with modern AI solutions.
Integrating AI into existing workflows often requires connecting cloud platforms, legacy systems, identity services, APIs, and business applications. Without a clear integration strategy, organizations create disconnected AI experiences that deliver limited value.
A practical approach is to begin with high-impact workflows, identify integration requirements early, and build scalable architectures that support future AI expansion.
5. Choosing the Right AI Integration Model
It is not mandatory to have an autonomous AI agent in every organization. One should carefully evaluate whether they need:
- Traditional API-based automation
- AI copilots that assist users
- Agentic AI capable of taking actions independently
- Retrieval-Augmented Generation (RAG) solutions that provide answers based on trusted enterprise knowledge
For identity and access management (IAM) environments, RAG often delivers immediate value by helping teams search policies, access reviews, compliance documentation, and governance procedures without exposing organizations to unnecessary automation risks.
6. Securing AI Agents and Non-Human Identities
One of the fastest-growing security challenges is the rise of AI agents operating with machine credentials.
AI agents increasingly access applications, retrieve data, execute workflows, and make decisions. However, many organizations manage these identities with the same informal practices used for scripts and service accounts. Every AI agent should be treated as a non-human identity.
Organizations should:
Register AI agents within identity and access management (IAM), IGA, or PAM systems.
- Enforce least-privilege access
- Rotate credentials regularly
- Monitor agent activities and sessions
- Audit all privileged actions
- Without proper controls, AI agents can quickly become high-value attack targets.
Final Thoughts
The biggest barriers to AI adoption are not model performance or technology limitations. They are governance, data quality, integration complexity, compliance requirements, and identity security.
Organizations that establish governance early, protect sensitive data, and manage AI agents as controlled digital identities will be far better positioned to scale AI initiatives confidently. As AI becomes embedded into critical business workflows, success will depend on treating governance and identity as foundational requirements, not afterthoughts.
Ready to Integrate AI Into Your Business Workflows? One of the top cybersecurity service-providing firms, TechDemocracy helps organizations identify risks, establish the right controls, and build a roadmap for responsible AI adoption.
Schedule a consultation with our experts at marketing@techdemocracy.com to assess your AI readiness and identify the right next steps for your organization.
FAQs
1. What is the biggest challenge organizations face when integrating AI into workflows?
The biggest challenge is not the AI technology itself. Most organizations struggle with governance, data quality, security, compliance, and integration with existing business systems. Without these foundations, even promising AI projects can fail to deliver value.
2. Why is AI governance important?
AI governance establishes the policies, processes, and accountability structures needed to ensure AI is used responsibly. It helps organizations manage risks, maintain compliance, improve transparency, and support audit requirements.
3. How can organizations protect sensitive data when using AI?
Organizations should classify sensitive data, document AI data flows, implement access controls, monitor usage, and ensure AI systems comply with applicable privacy regulations. Sensitive customer, employee, and intellectual property data should never be exposed to unauthorized AI systems.
4. How does poor data quality affect AI performance?
AI models learn and generate insights based on the data they receive. Inaccurate, incomplete, or outdated data can lead to incorrect recommendations, poor decisions, and unreliable business outcomes.
5. What is the best way to start integrating AI into existing workflows?
Begin with a well-defined business problem rather than adopting AI for its own sake. Identify high-impact workflows, evaluate the required data and integrations, establish governance controls, and start with small pilot initiatives before scaling.
6. What is the difference between AI agents and rule-based automation?
Traditional automation follows predefined rules and workflows. AI agents can reason, make decisions, interact with multiple systems, and adapt to changing inputs. While more powerful, AI agents also introduce greater governance and security requirements.
7. When should organizations use RAG instead of an AI agent?
Retrieval-Augmented Generation (RAG) is often a better choice when users need accurate responses based on trusted enterprise knowledge. For IAM, compliance, policy management, and knowledge-heavy use cases, RAG can provide reliable answers without granting autonomous decision-making capabilities.
8. Why should AI agents be treated as non-human identities (NHIs)?
AI agents access applications, data, and business systems just like employees and contractors. Treating them as non-human identities (NHIs) allows organizations to apply identity governance, least-privilege access, credential management, monitoring, and auditing controls.
9. How do IAM and PAM support secure AI adoption?
Identity and Access Management (IAM) and Privileged Access Management (PAM) help organizations control what AI agents can access, enforce least-privilege permissions, manage credentials, monitor activities, and reduce the risk of unauthorized actions.
Recommended articles
Agentic AI Governance for Modern Organizations: Trends Shaping 2026
Take Your Identity Strategy
to the Next Level
Strengthen your organization's digital identity for a secure and worry-free tomorrow. Kickstart the journey with a complimentary consultation to explore personalized solutions.